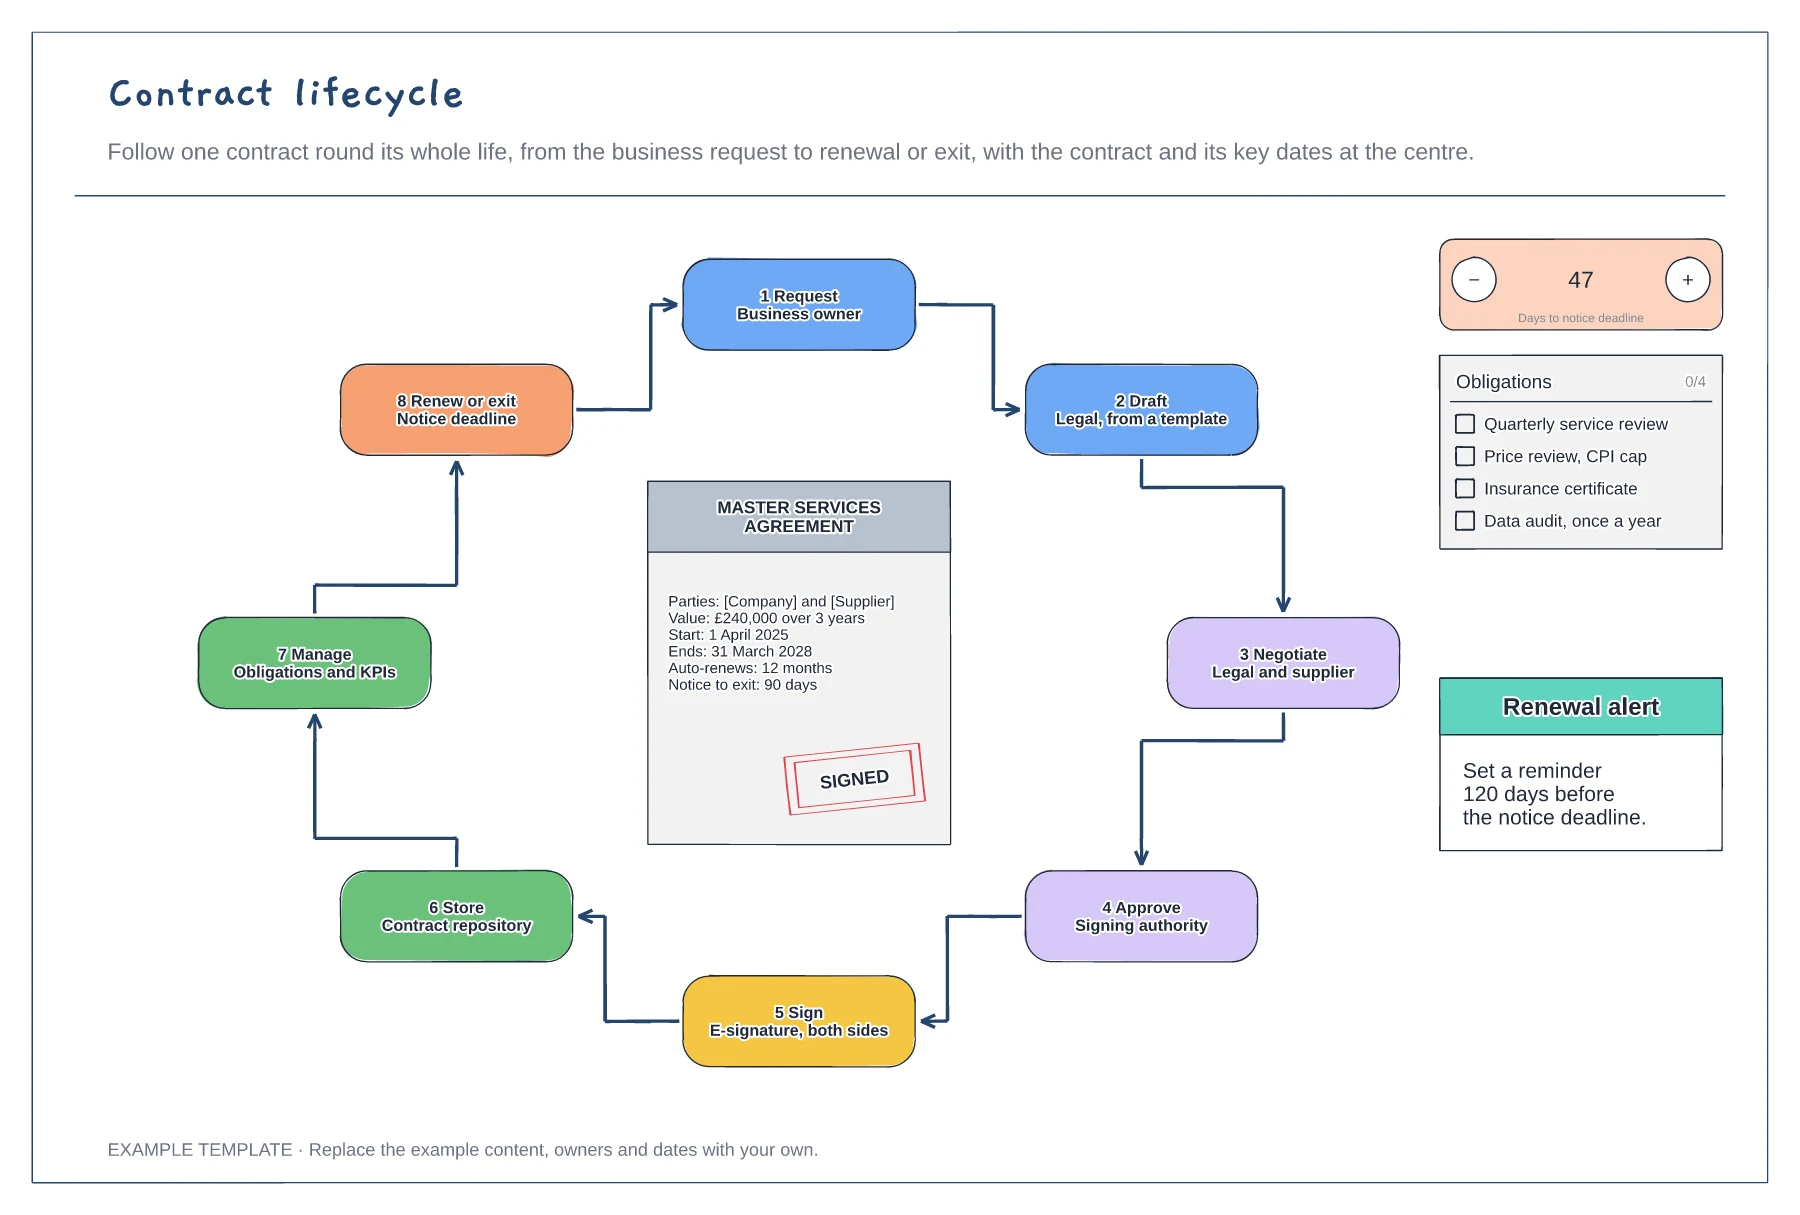
Legal and risk
Contract lifecycle template
Eight stages in a loop with owners · Contract summary with key dates · Notice countdown and obligations list
Preview and use template →Third-party risk management is about spending your checking effort where suppliers could do the most harm. This board sorts 572 suppliers into a four-tier pyramid, from eight critical suppliers at the top to hundreds of low-risk ones at the base, and sets out in a matrix which checks each tier gets: security questionnaires, assurance reports, financial checks, audits, data terms, exit plans and review frequency.
This is a planning example, not legal advice. Check your own policies, advisers and the local rules that apply to you.
No account needed · Opens as your own editable page
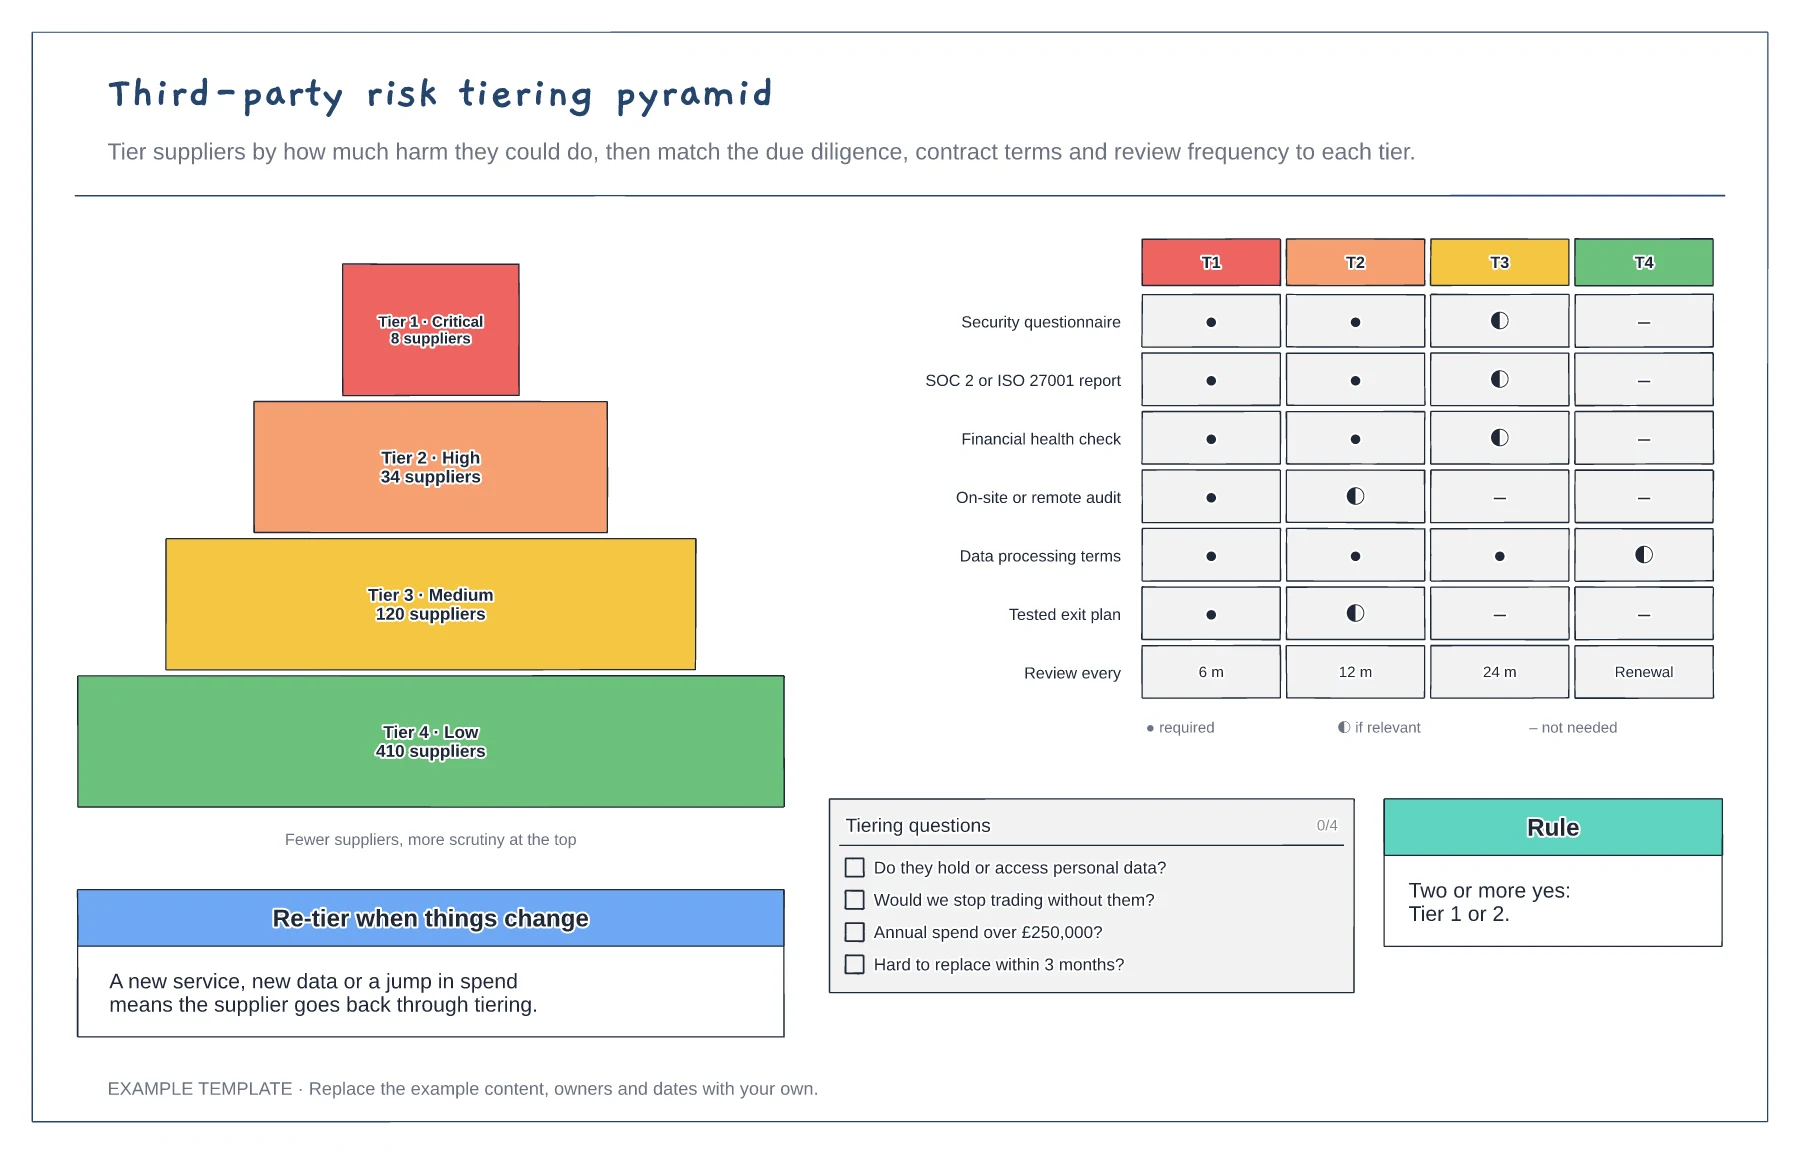
Pick a few questions that show how much harm a supplier could do, such as access to personal data or how hard they are to replace.
Run each supplier through the questions and count how many land in each tier. Most should be at the base.
Decide which checks and contract terms each tier needs and how often you review them, then apply them at onboarding and renewal.
A filled circle means the check is required for that tier, a half circle means it applies if relevant and a dash means it is not needed.
No. Open the template and edit it in your browser. Your work saves on this device. An account is optional if you want to sync your workspace.
Yes. Use Export in the editor to save a PNG, SVG or PDF, or download an editable .epicdraw backup.
Eight stages in a loop with owners · Contract summary with key dates · Notice countdown and obligations list
Preview and use template →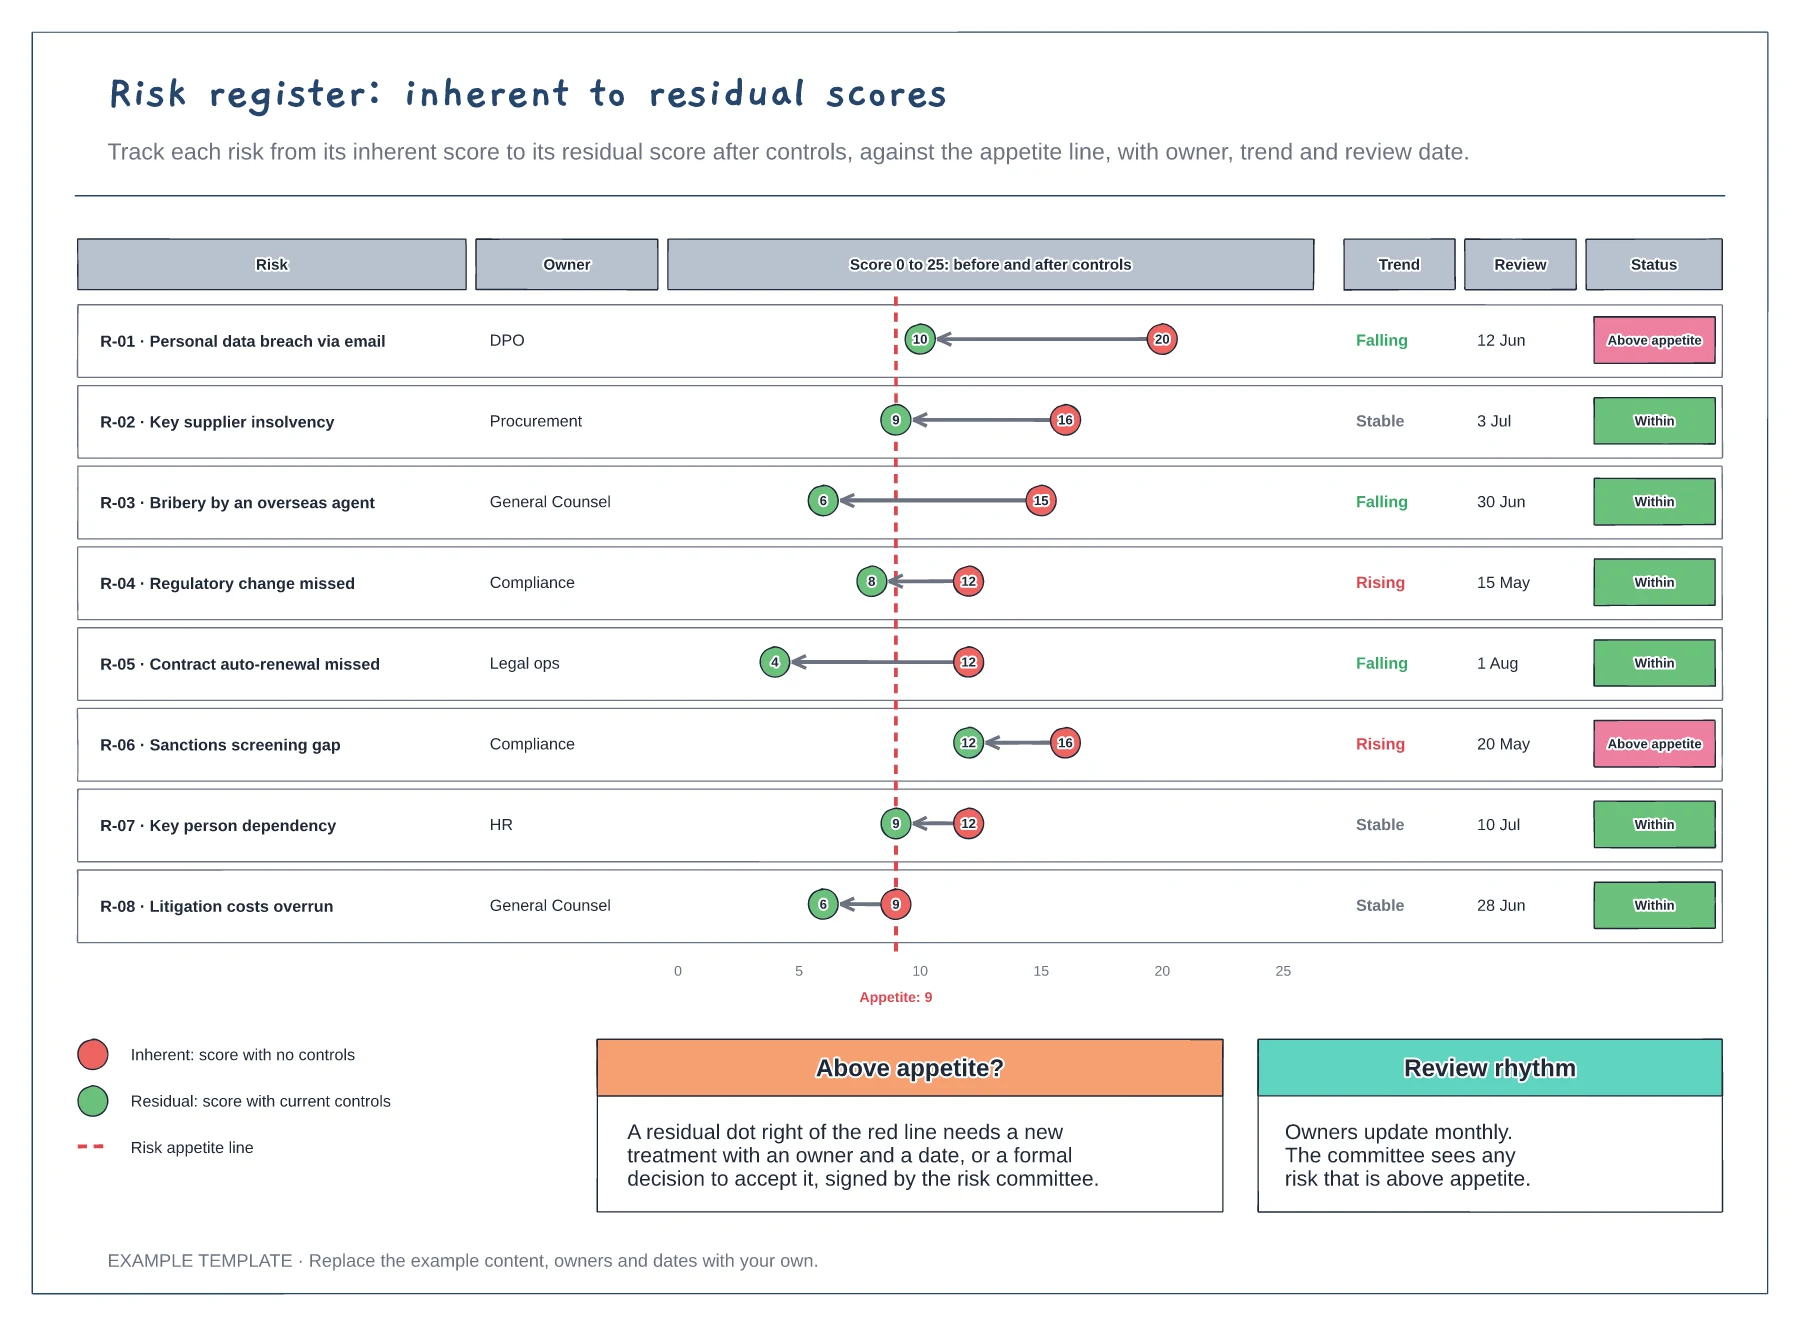
Eight risks with owners and review dates · Inherent to residual bars on one scale · Risk appetite line and status flags
Preview and use template →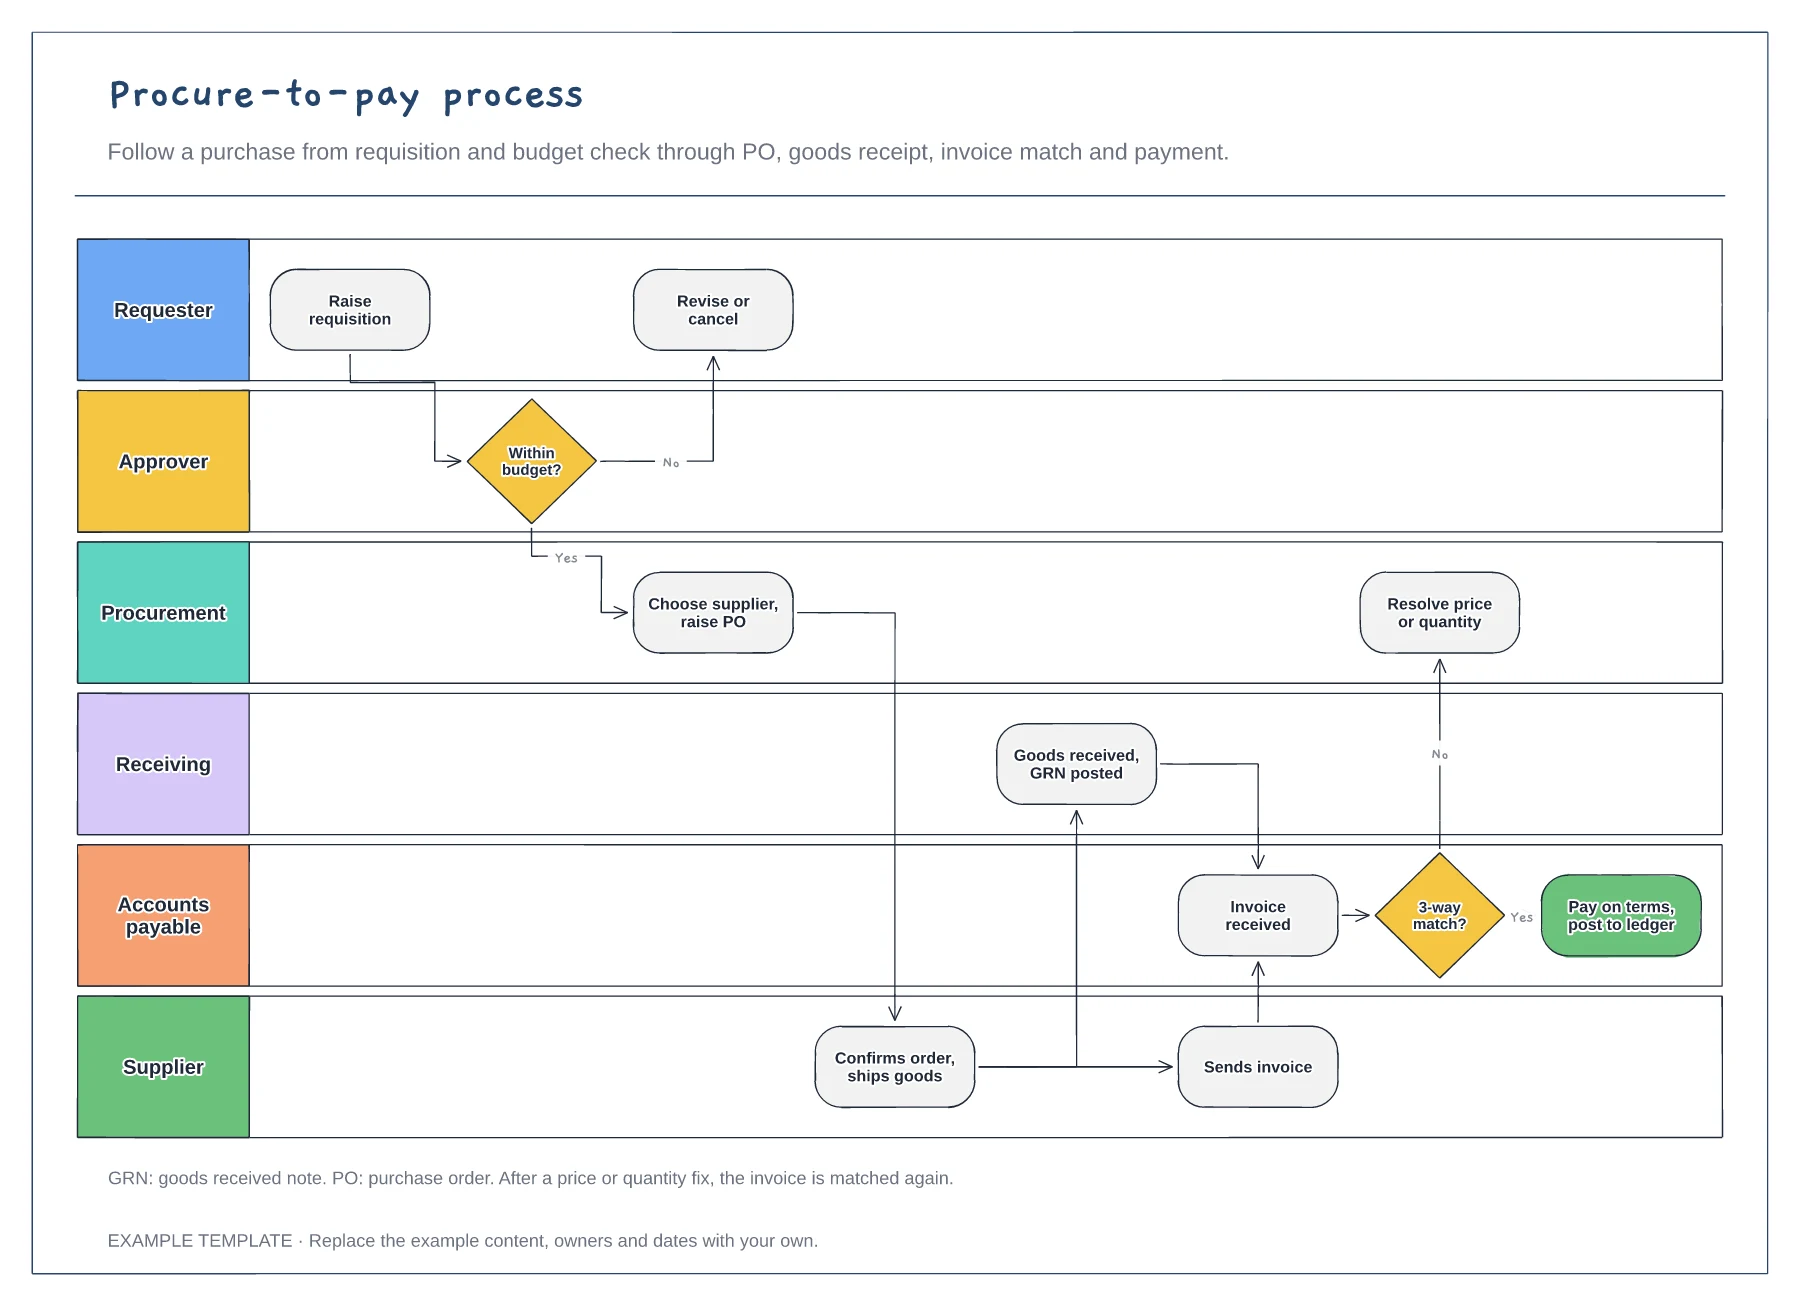
Six lanes from requester to supplier · Budget check and purchase order · Goods receipt, invoice match and payment
Preview and use template →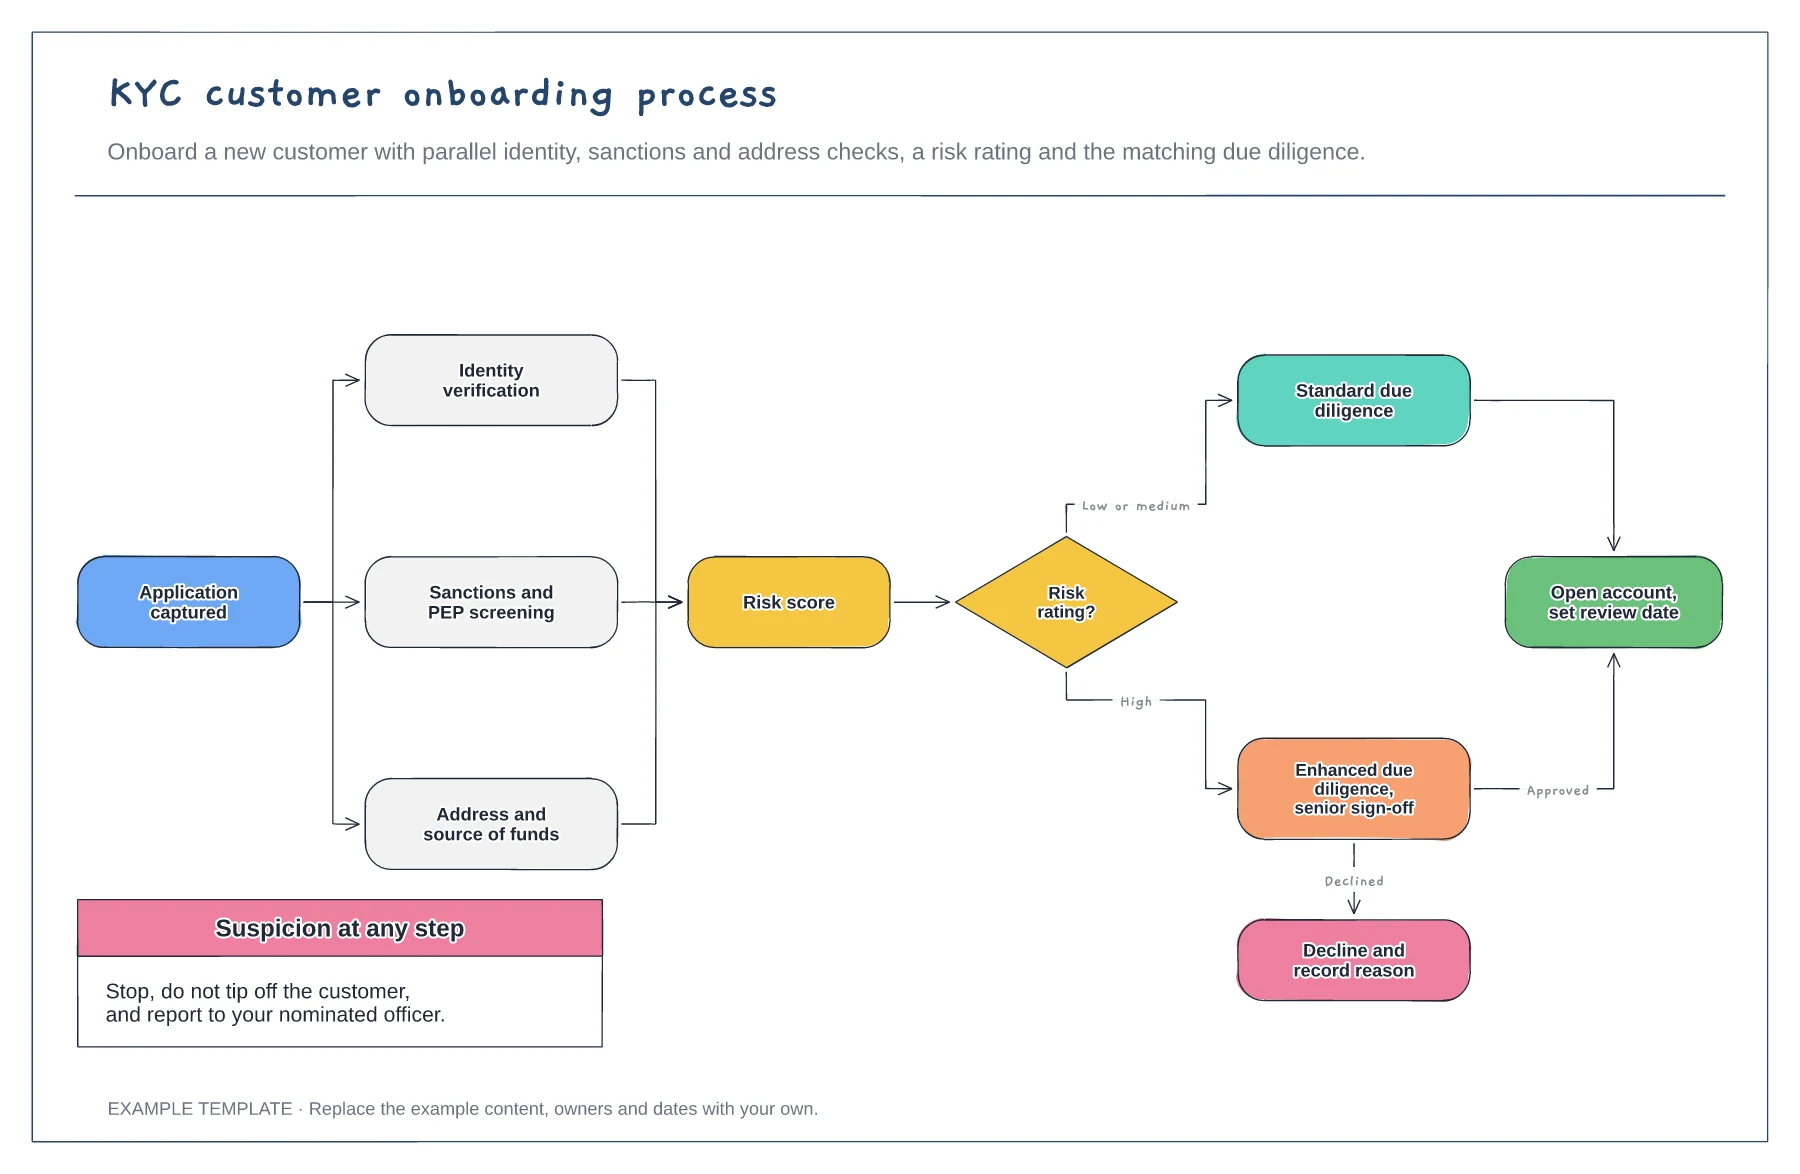
Three checks run in parallel · Risk rating with two due diligence routes · Decline route and suspicion note
Preview and use template →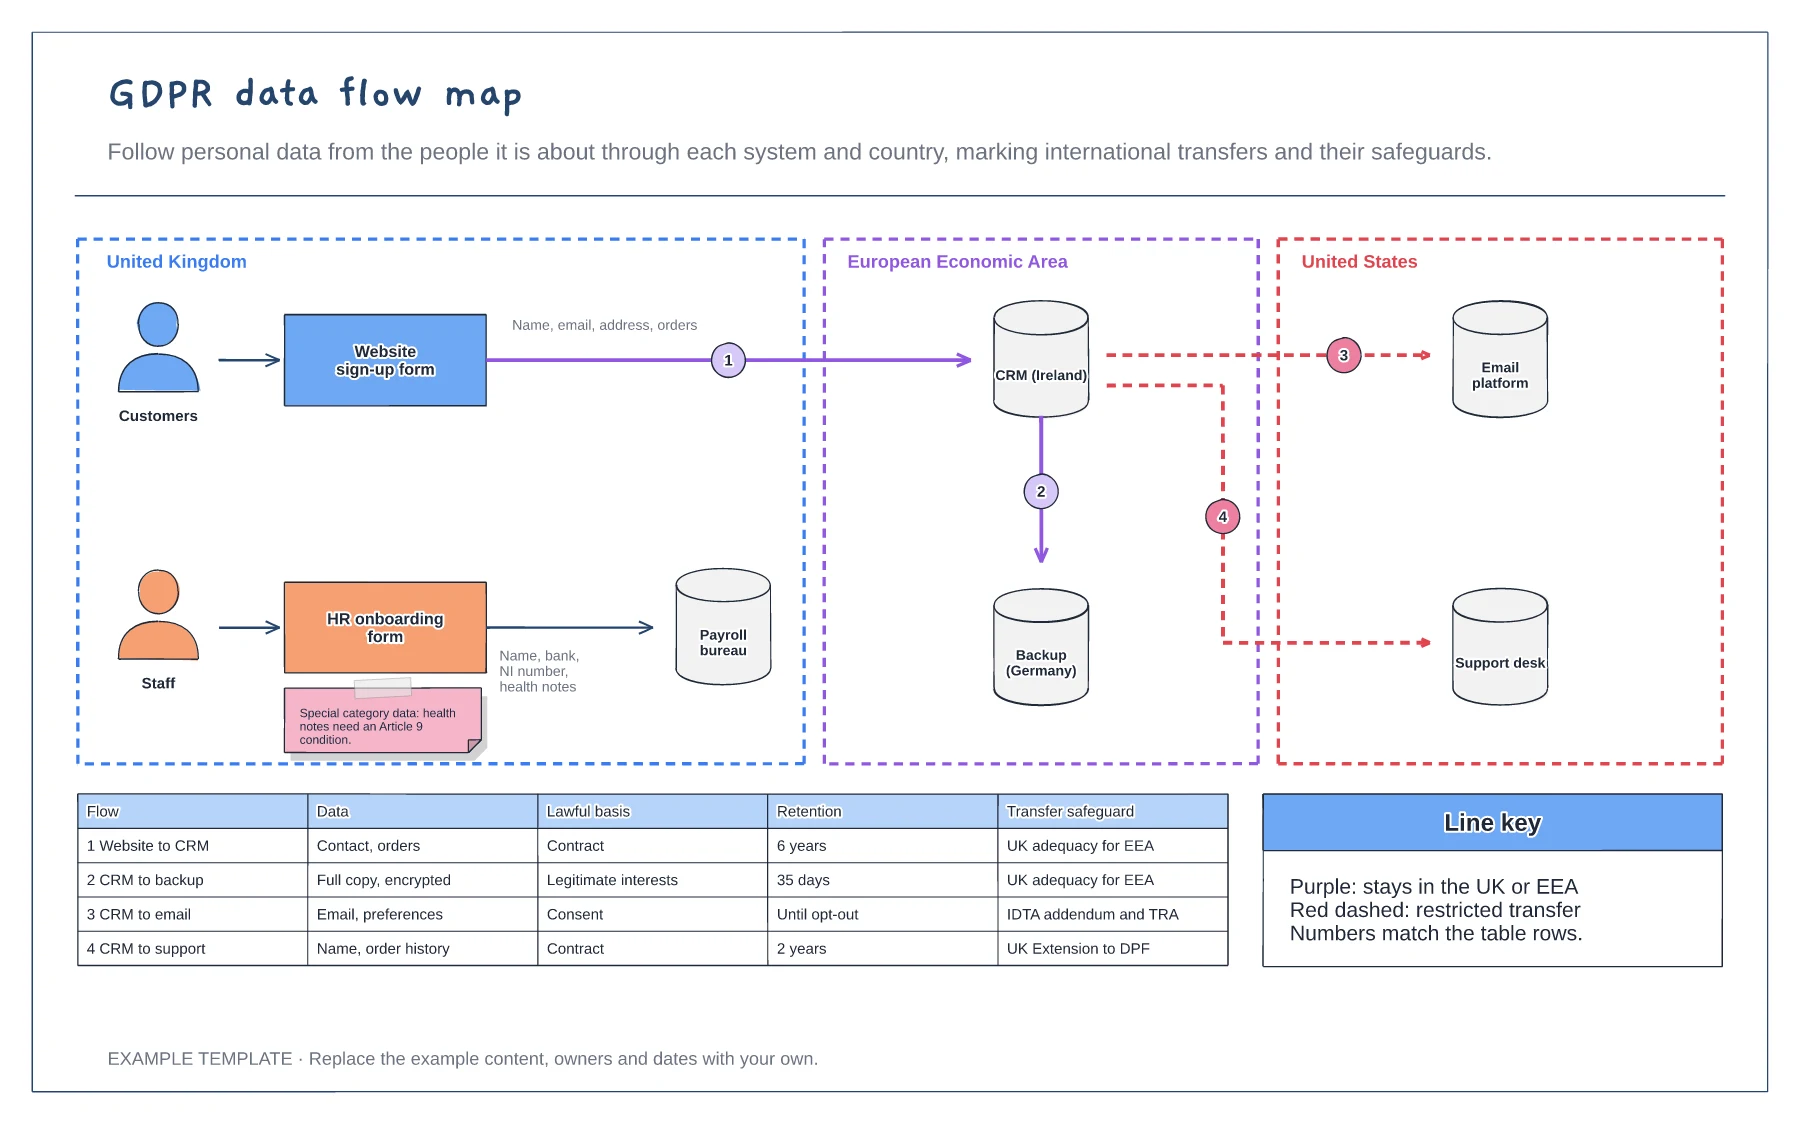
Systems grouped by country · Numbered flows with restricted transfers marked · Lawful basis, retention and safeguard table
Preview and use template →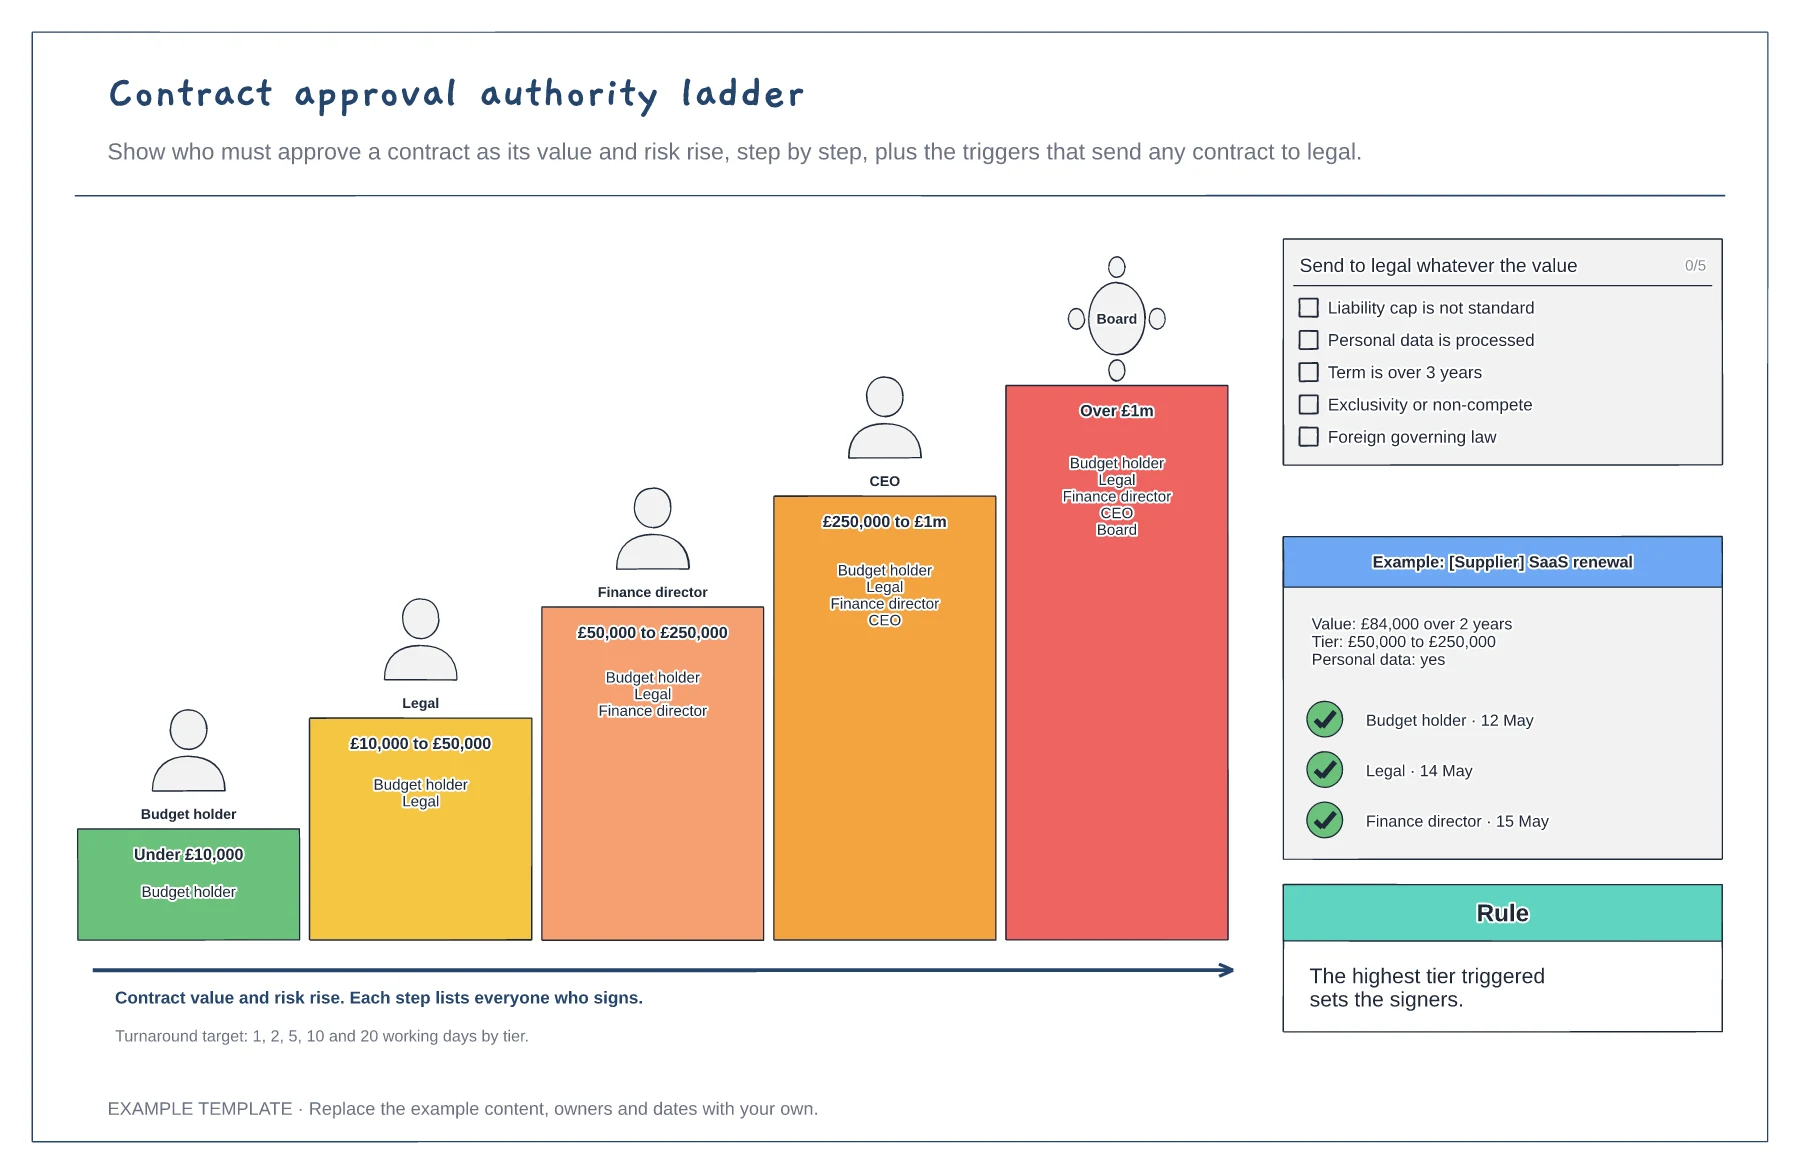
Five value tiers with cumulative signers · Risk triggers for legal review · A worked approval example
Preview and use template →